

Managed cloud
The operations loop under every sector.
Details
By industry
One operating model, tuned to what matters most in your sector: compliance, uptime, data residency, and scale. Here's how that lands in each.
By sector
The infrastructure, the operations loop and the evidence are the same everywhere. What changes is what matters most: privacy and audit in healthcare, continuity and proof in finance, velocity in software, governance in the enterprise, and in water, a regulatory wave with dates on it.
01 · Healthcare
Privacy, audit, uptime.
Clinical and patient-facing systems carry real-world consequences when they fail, and they sit under strict privacy and audit expectations. Downtime and data exposure are not options.
We operate these workloads with availability and protection built in, and keep the evidence auditors ask for ready by default.
How we operate for you
The services that carry it
Water & critical infrastructure
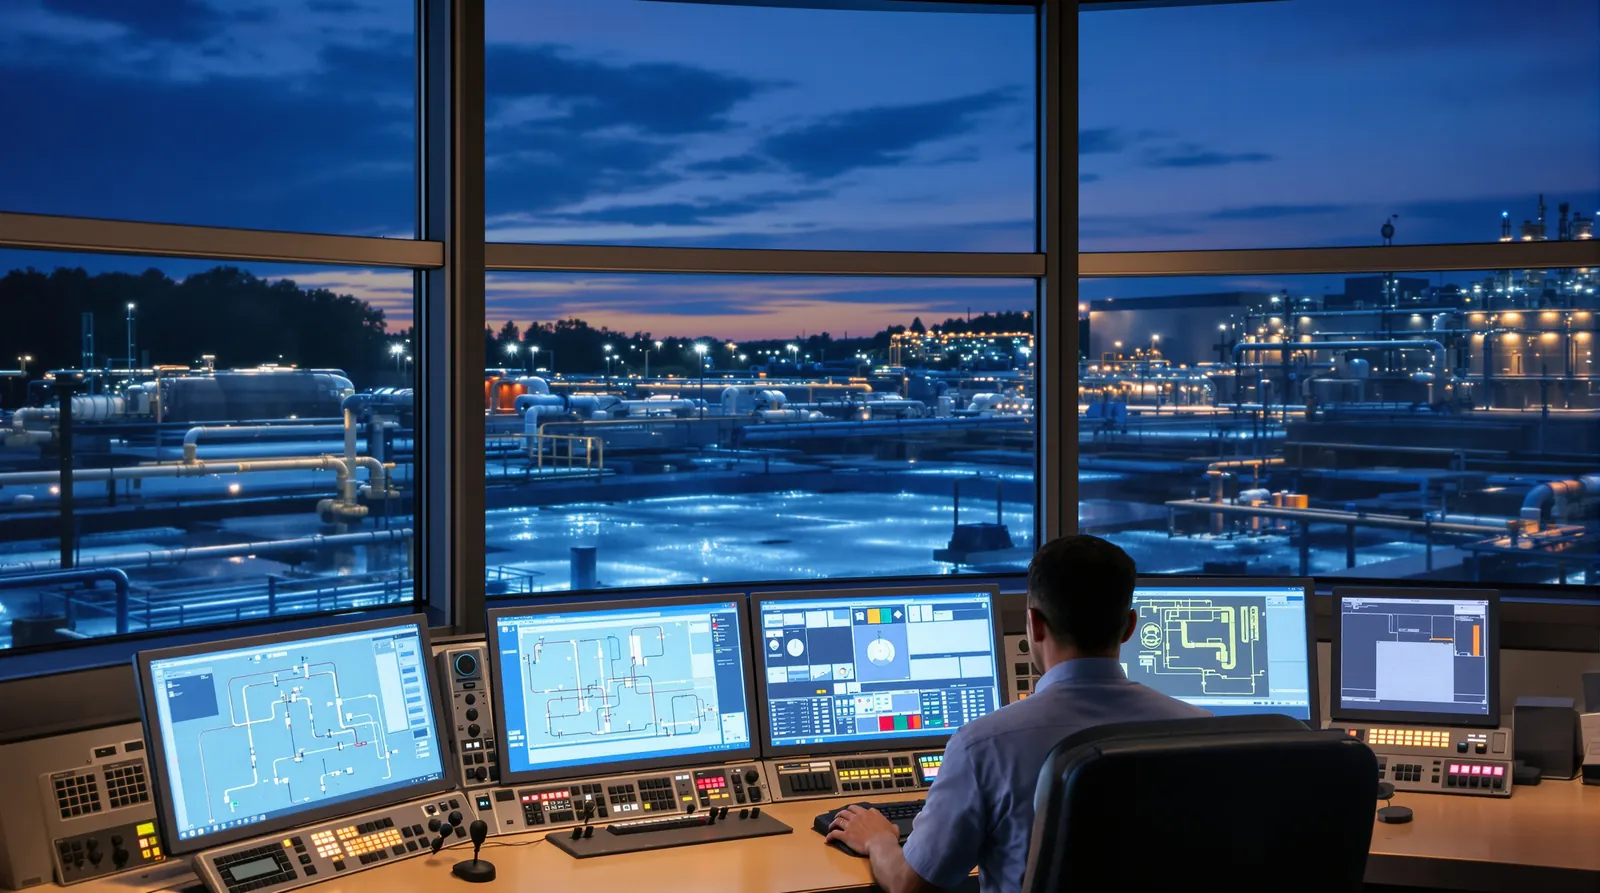
Control systems stay in their own world, operated with your OT vendors. Every connection to them runs through a monitored gateway: authenticated, logged, reviewed. The business estate runs on CloudPresto infrastructure, off the operational network, with geo-redundant backups behind it. Segmentation is the control regulators named; this is what it looks like.
The mandate, mapped · eight capabilities and what we run for each
From the capability brief, September 2026
1
Named accountability
Board-ready reporting and audit-ready records of every change and incident.
State designated-officer rules · CISA CPG leadership goal
2
A real inventory
Estate discovery: servers, services, remote links, IT/OT connections, documented and kept current.
SDWA §1433 (AWIA) · CISA CPG asset inventory
3
Closed front doors
MFA on every administrative path, credential policy, exposed controllers behind a monitored gateway.
State MFA rules · CISA CPG account security
4
IT/OT separation
Segmentation designed, hosted and monitored; business systems off the operational network.
CISA CPG segmentation · state OT/IT rules
5
Eyes on the network
24/7 monitoring with log collection and retention aligned to the audit trails required of you.
State utility-commission rules · CISA CPG detection
6
Rehearsed response
A defined incident process with the reporting clocks built in: state and, once in force, CISA.
CIRCIA (final rule pending) · state reporting · AWIA ERPs
7
Provable recovery
Geo-redundant backups with isolated copies; restores tested on a schedule with recorded times.
EPA cyber drill scenario · CISA CPG backup and recovery
8
Suppliers held to the standard
Contractual security terms; access that is controlled, logged and reviewable.
CISA CPG supply chain · state third-party standards
Common ground
Whatever the stakes, the foundation is the same: our own infrastructure, operated to one enterprise standard, with the evidence produced as a by-product of running it.
01
Data residency
Our own cloud across the US, EU and Asia gives you real control over where data lives.
02
Compliance-aligned
Controls aligned with SOC 2, ISO 27001, CIS and HIPAA; certifications published when achieved.
03
Always-on operations
24/7 monitoring with defined escalation, on infrastructure held to a 99.9% uptime standard.
04
Proven recovery
Resilience engineered into the architecture and validated in regular failover drills.
How we work
The path in is the same in every sector. It starts with a structured review of your estate against the standards you are held to, and ends in a plan your board can act on.
01
Readiness assessment
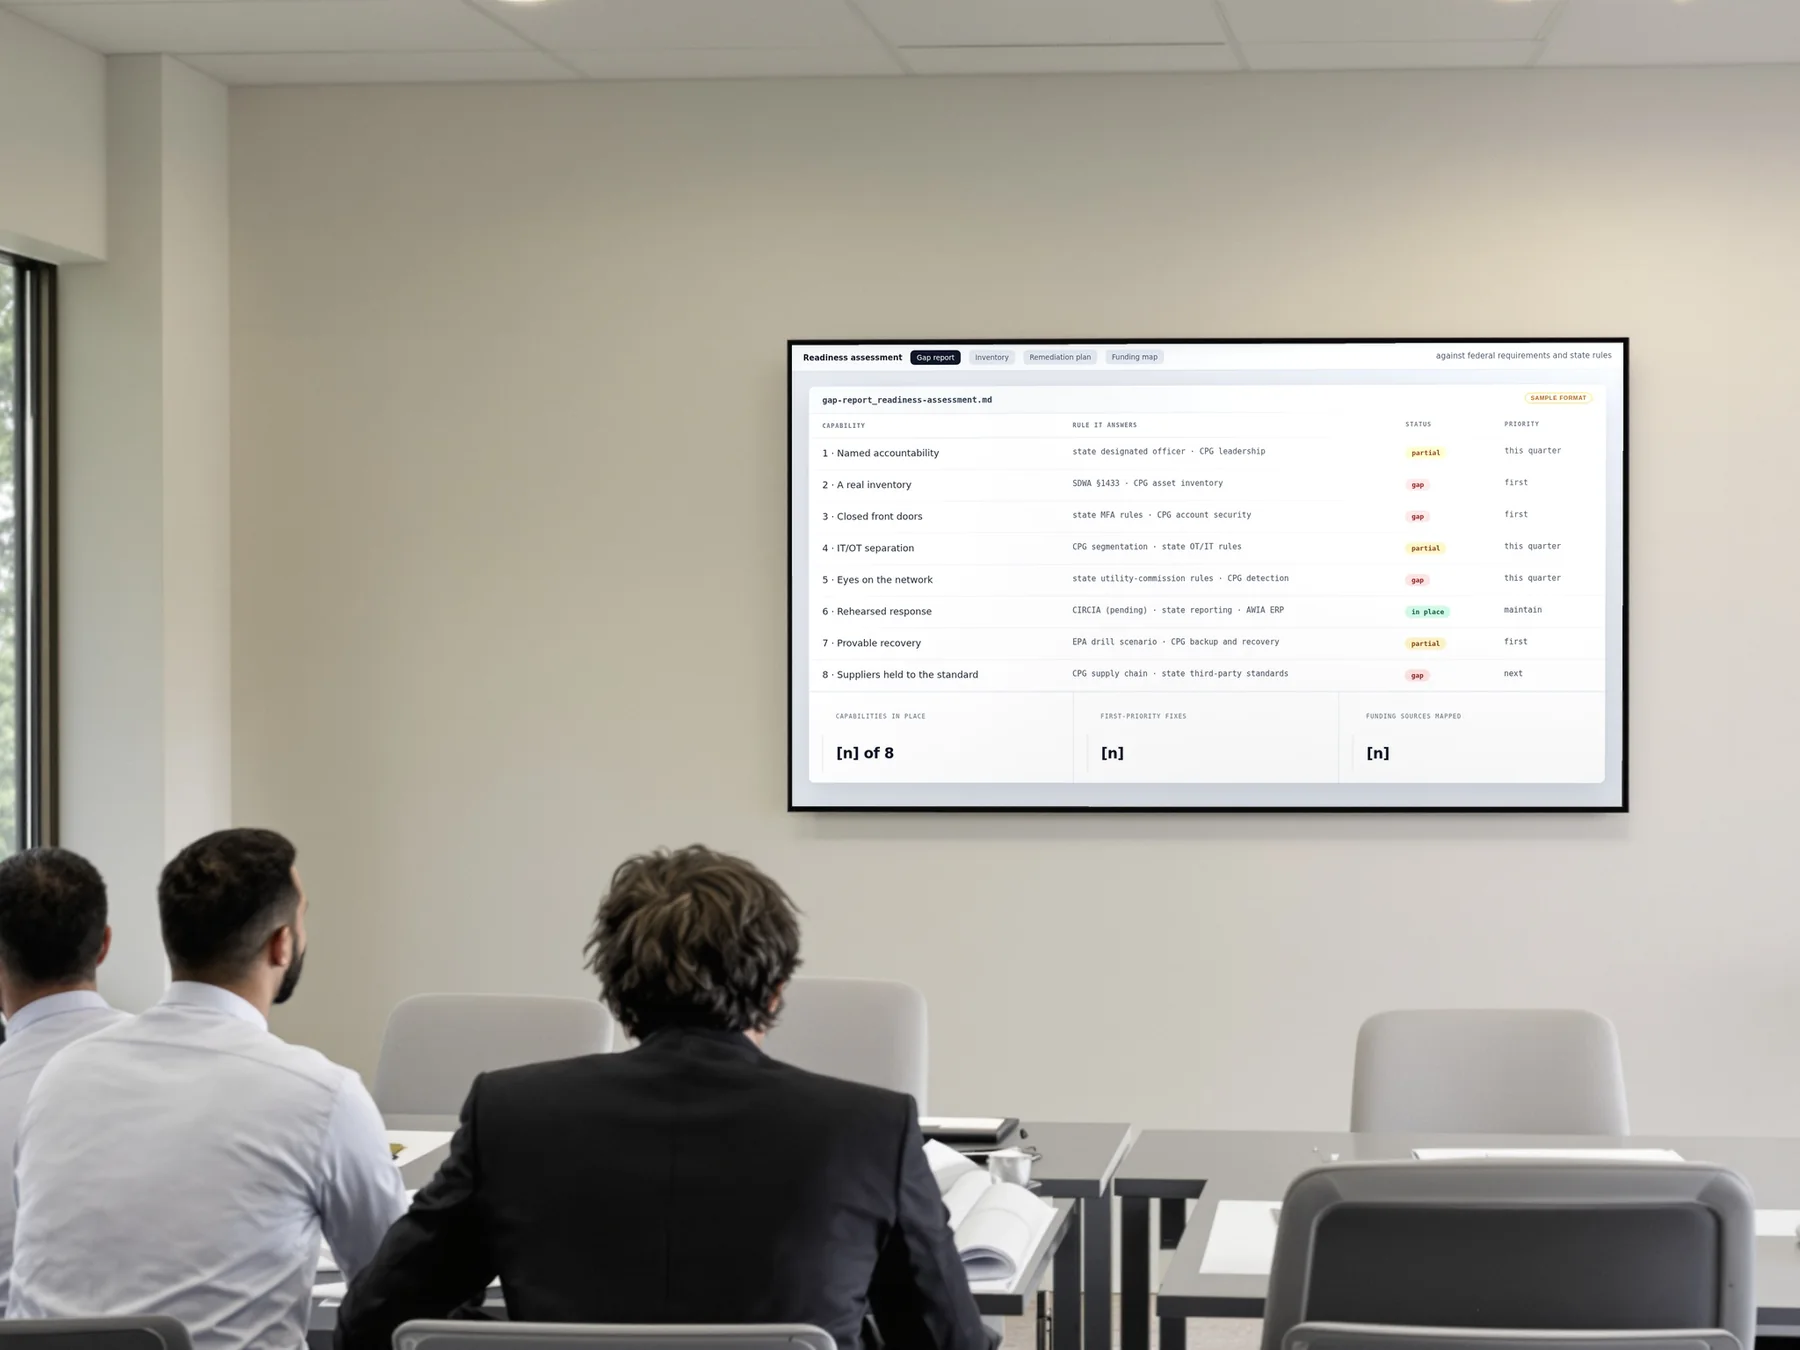
Your estate reviewed against the frameworks and rules that apply to you. You receive a gap report and a prioritised plan.
02
Remediation
The prioritised fixes, executed: hardening and access control, segmentation, monitoring and log retention, geo-redundant backup with a tested first restore.
03
Managed operations
We operate the estate: monitoring, incident response, change management, backup verification, and the recurring reports your audits require.
04
The evidence, as you go
As deadlines and audits arrive, the controls, operating records and evidence are already in place.
Get started
We show you how we would operate it, with the risks named up front. For water utilities, the readiness assessment is the right first step.
What to have ready · in whatever state it exists
01
The network picture
Any current diagram or description of how business systems, control or core systems and remote connections relate.
02
The access list
Who can reach your systems remotely: integrators, vendors, support, anyone with a login.
03
The last assessment and plan
The most recent risk assessment and response plan, whatever framework produced them.
04
Backup reality
Where backups go, how often, and the date of the last restore anyone actually performed.
Go further
Collection
Access, encryption and the security posture, in four guides.
Guide
SOC 2, ISO 27001, HIPAA alignment, with evidence collection built into operations.
Guide
The CloudPresto service stack: what to start with and what to add.
Guide
What to audit, prepare and validate before moving workloads.

