

Managed cloud
The operations loop the audit trail is written from.
Details
Security
Access controls, encryption, incident response, continuous monitoring. Security isn't an add-on. It's the foundation everything runs on.
How it works
We operate every layer your workload sits on, and every layer writes what it does into the same immutable record: who, what, when, why. Security is not a product we add. It is how the estate is run, and the record is the evidence.
Your workload
Five layers, outside in, around your workload. Every one writes what it does into the same record: who, what, when, why. Choose a layer.
Change control · what every production change goes through
No exceptions
01
Request
What changes, on which systems, in which window, how it rolls back. Written before anything is touched.
02
Assess and approve
Risk graded, rollback plan attached, approval recorded with who gave it.
03
Change
Executed inside the window through scoped, logged administrative access.
04
Verify and close
Post-change checks and monitoring confirm the outcome. The entry closes the trail.
What is built in
Hardened from day one, not bolted on. Six domains on every system we operate, with the situation each is there for, all writing to the same audit trail.
CIS-benchmarked builds, network least-privilege by default, automated patching.
Built for · Servers that drifted from how they were built.
MFA on all administrative access, SSO, logged sessions, automated offboarding.
Built for · Shared credentials nobody has rotated.
AES-256 at rest, TLS 1.3 in transit, separate key hierarchies for production and backup.
Built for · Backups encrypted with the same key as production.
Centralised logging, anomaly detection, defined response playbooks by severity.
Built for · An intrusion found by the customer.
Segmentation, WAF and DDoS protection at the edge, zero-trust policies inside.
Built for · A flat network where one host reaches everything.
Immutable change trails and evidence packages for SOC 2, ISO 27001 and customer frameworks.
Built for · An audit that starts with a scramble for screenshots.
Compliance
We practise controls aligned with SOC 2, ISO 27001 and CIS benchmarks, and technical safeguards for HIPAA environments. Formal certifications are published only when achieved. What we share instead is the control evidence itself, during your security review.
Control ledger · framework alignment and the evidence behind it
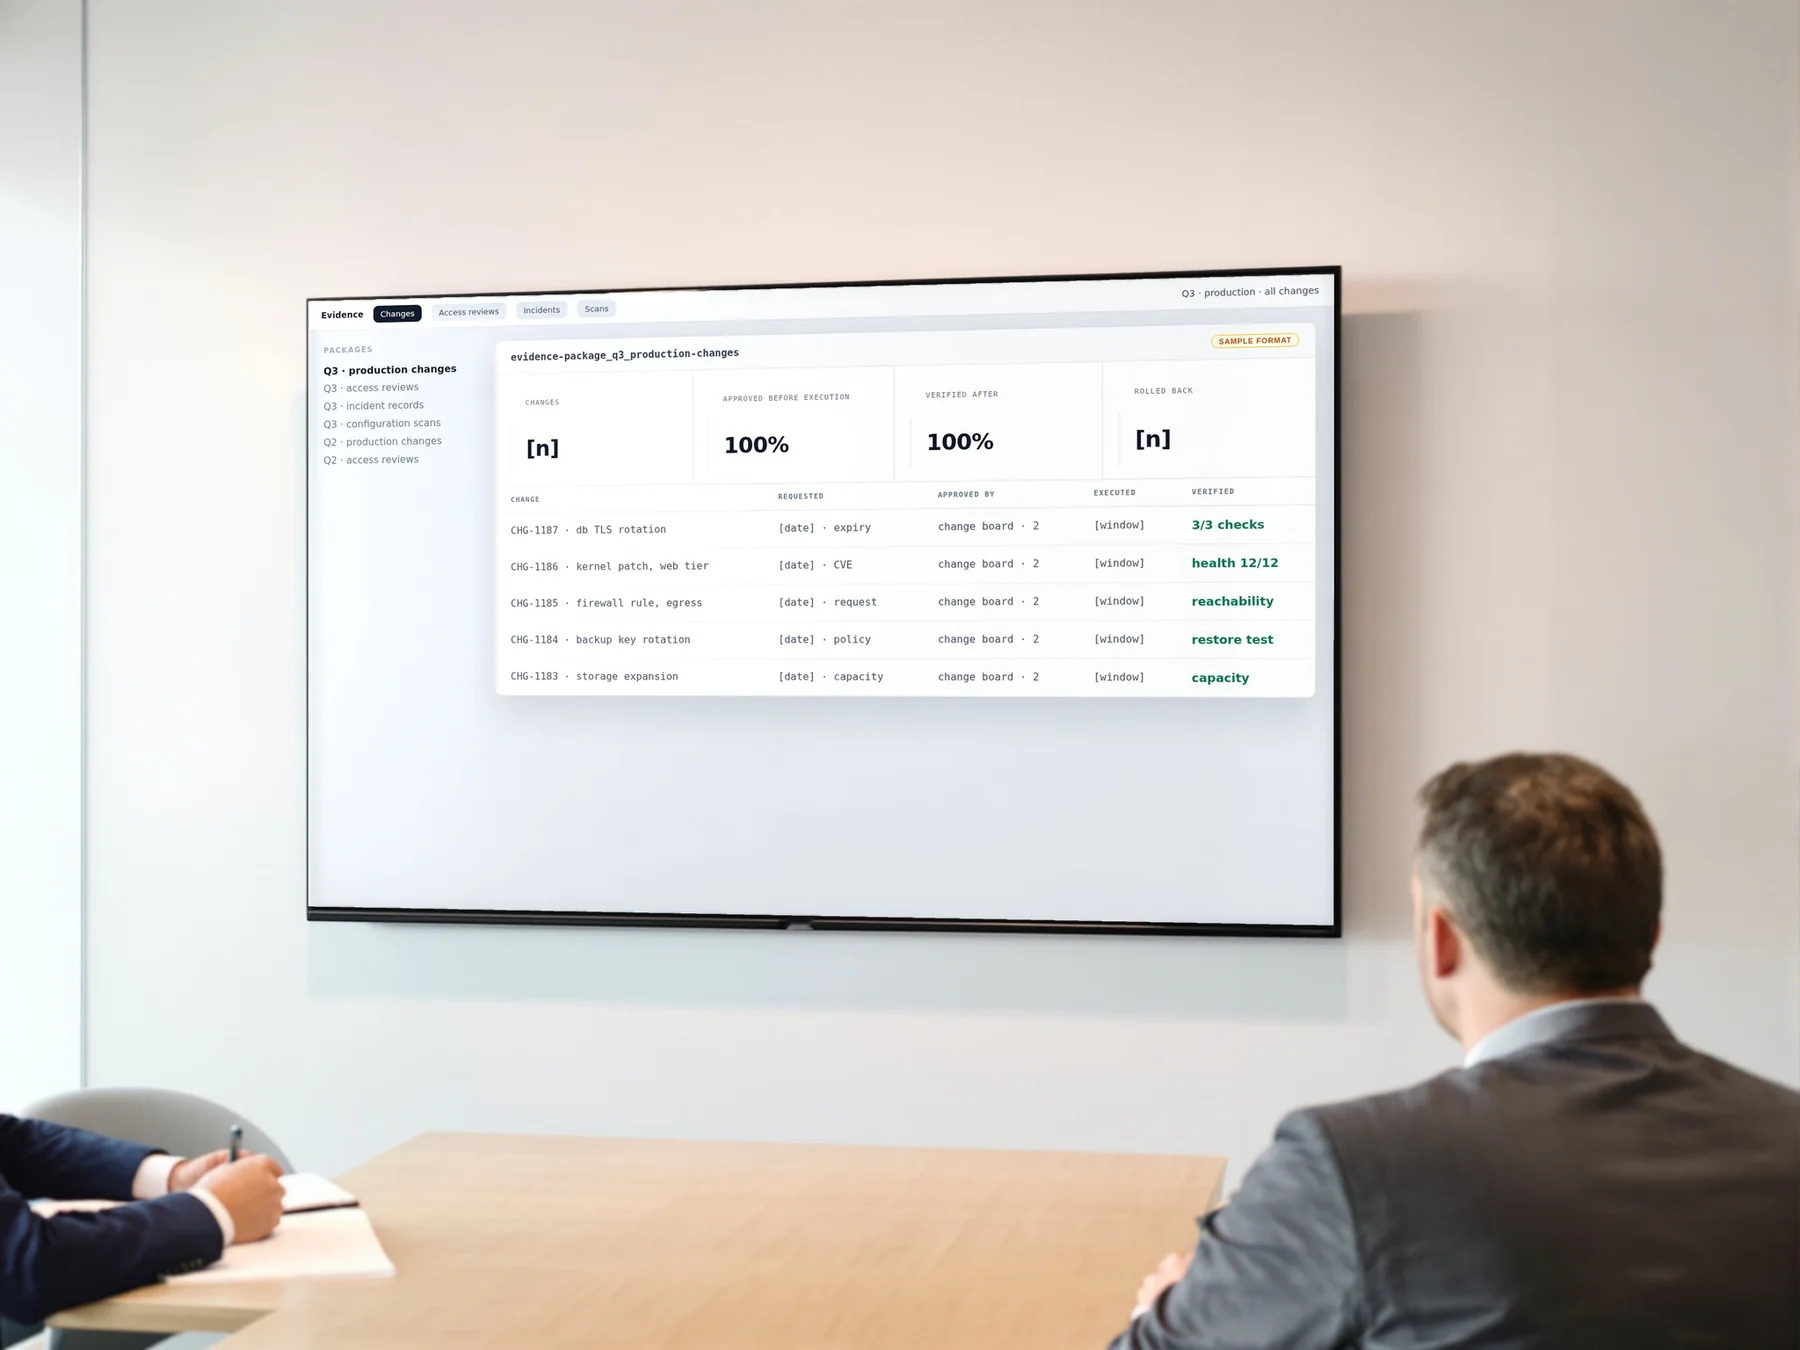
Evidence packages on request, any period within retention
| Framework | What we align to | Evidence available |
|---|---|---|
| SOC 2 | Controls aligned to the Trust Service Criteria | Change logs, access reviews, incident records, monitoring evidence |
| ISO 27001 | ISMS-aligned operational controls | Risk assessments, control documentation, audit trails |
| CIS Benchmarks | Infrastructure hardened to CIS Level 1+ | Configuration scan results, remediation records |
| HIPAA | Technical safeguards for protected environments | Access controls, encryption evidence, audit logs |
Who secures what · on CloudPresto cloud
We secure
The infrastructure and its operation
Together
Agreed in the engagement
You secure
What only you can
Incidents and patching
A security event follows a defined playbook from detection to review. A vulnerability follows a defined path from discovery to a closed ticket, inside a remediation window set by its severity. Both loops write to the same trail.
Incident response · by severity
01
Detect and classify
Event classified by severity. P1 security incidents are triaged on priority.
02
Contain
Affected systems isolated, credentials rotated, attack surface minimised while the investigation proceeds.
03
Eradicate and recover
Root cause eliminated, systems restored from a known-good state, integrity verified before return to service.
04
Post-incident review
Timeline, root cause and preventive actions documented for every event. Lessons applied to detection rules and playbooks.
Vulnerability management · tracked as a KPI
CVSS 9.0–10.0 · remediation within its defined window
Emergency change: patch or mitigation outside the scheduled window.
CVSS 7.0–8.9 · remediation within its defined window
Scheduled patch within the next change window.
CVSS 4.0–6.9 · remediation within its defined window
Included in the regular patch cycle.
CVSS 0.1–3.9 · remediation within its defined window
Addressed during maintenance cycles.
The review
A security review before any engagement, with your team or your auditors in the room. We walk through the controls, share the evidence, and answer the specifics.
01
Documentation
Security architecture, policies and the control set, sent ahead so the meeting starts with questions.
02
Architecture walkthrough
Tenant isolation, network segmentation, encryption and key handling, access governance, on the real estate.
03
Control evidence
Change logs, access reviews, incident records and configuration scans for the period you name.
04
Penetration testing
Customer-initiated testing of managed environments, coordinated in advance. Findings reviewed jointly and tracked to closure.
Get started
Tell us what you need to verify and who needs to see it. We walk through the controls, share the evidence and answer your team's questions.
What the review covers
01
The control set, documented
Architecture and policies your auditor can file.
02
Evidence for the period you name
Change logs, access reviews, incident records, scan results.
03
Your open questions, answered in writing
Including the ones we could not answer in the room.
Go further
Collection
Access, encryption and the security posture, in four guides.
Collection
Threat monitoring, network architecture, compliance and vulnerability management.
Guide
SOC 2, ISO 27001, HIPAA alignment, with evidence collection built into operations.
Guide
Continuous scanning, risk-ranked remediation and patch compliance as a KPI.

